
World Password Day 2026: Why AI is making passwords obsolete faster than expected

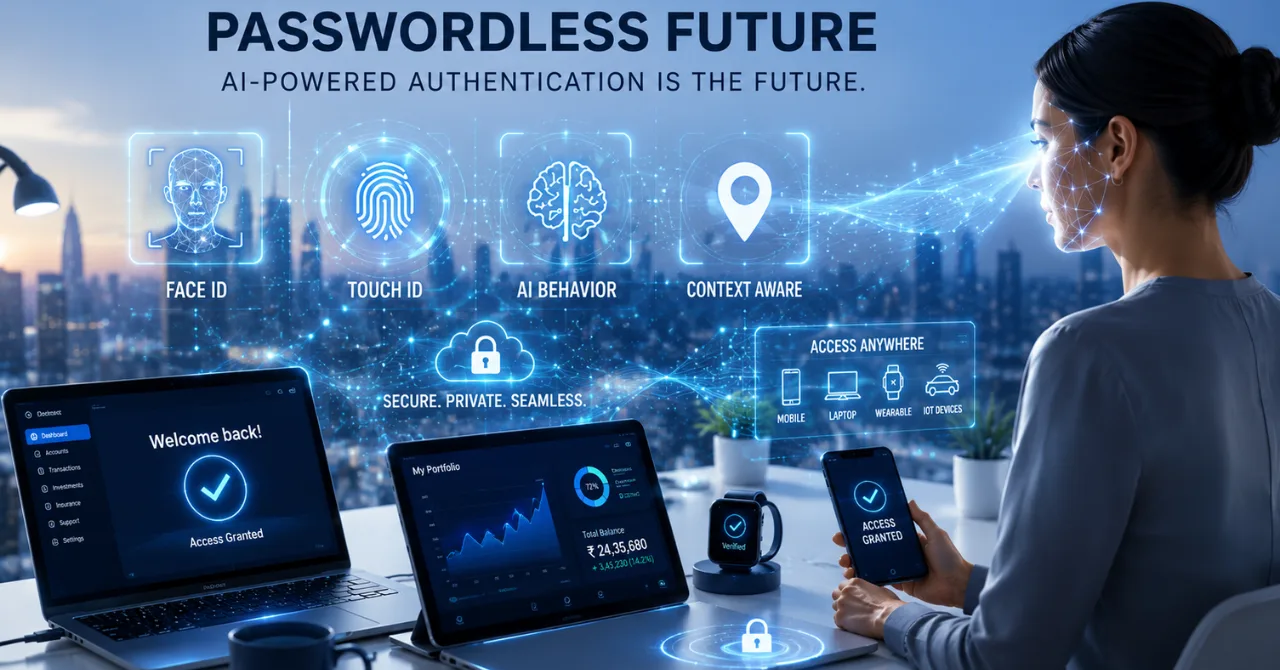
World Password Day, observed on 7 May, arrives in 2026 with a sharper sense of urgency. Passwords once formed the backbone of digital security. Today, they are increasingly viewed as one of the weakest links in enterprise defence.
The conversation is no longer limited to weak passwords, forgotten credentials or password reuse. The bigger challenge now is identity itself. Human identities. Machine identities. AI agents. API tokens. Autonomous systems quietly access enterprise applications behind the scenes.
Across India’s rapidly digitising economy, security leaders are warning that traditional authentication methods are struggling to keep pace with AI-driven threats and expanding digital ecosystems. Passwordless authentication, passkeys, multi-factor authentication (MFA), and zero trust frameworks are quickly moving from optional upgrades to operational necessities.
What makes this transition especially important is the growing presence of non-human identities inside organisations. AI agents are increasingly making decisions, accessing sensitive systems and interacting with customer data independently. That changes the security equation completely.
World Password day 2026 - Passwords are becoming the weakest point
Security experts agree on one thing: static passwords were never designed for today’s threat landscape.
Andrew Spangler, Senior Director, Security and Compliance, Harness, said organisations need to rethink identity security entirely rather than simply improving password habits.
“Passkeys and passwordless authentication need to become the default to eliminate shared secrets and reduce phishing risk at scale,” Spangler said. He added that long and unique passphrases, MFA and password managers remain essential foundations of modern security.
Spangler also pointed to a larger shift taking place inside enterprises.
“Security needs to become continuous, embedded and system-driven. Every access point, identity and interaction needs to be part of an active defence model that adapts in real time,” he said.
That shift is becoming critical as cybercriminals increasingly use AI and automation to launch credential attacks faster and at greater scale.
AI agents are creating a new identity crisis
A recurring theme across industry commentary this year is the rise of non-human identities.
Balaji Rao, Area VP, India and SAARC, Commvault, said enterprises are witnessing an “unprecedented expansion of digital identities” as AI agents become active participants in business operations rather than passive software tools.
“Every AI agent accesses user-specific data, workflows and multiple applications, and therefore, needs a unique identity and clearly defined access rights,” Rao said.
He added that strong encryption, MFA, multi-person approval mechanisms and centralised identity management are becoming mandatory as organisations deploy AI at scale.
The issue is particularly relevant in India, where enterprises are accelerating AI adoption across customer service, operations, analytics and software development.
The challenge? Most traditional identity systems were built for humans. Not autonomous AI systems operating continuously across multiple applications.
Enterprises are struggling with legacy authentication systems
Many organisations still depend on fragmented identity systems and legacy infrastructure. That creates blind spots.
Rizwan Patel, Global Head, Cloud, Infosec and Emerging Technologies, Altimetrik, said identity has now become the “primary attack surface” for modern enterprises.
According to Patel, the security perimeter has steadily disappeared as businesses expand across Cloud platforms, APIs and interconnected digital ecosystems.
“What makes this moment distinct is that the identity surface has expanded well beyond human users and now increasingly incorporates service accounts, API tokens, CI/CD pipelines and autonomous AI agents,” Patel said.
He warned that most non-human identities still operate without proper governance, often carrying standing privileges and infrequently rotated credentials.
That creates a serious but underappreciated enterprise risk.
Patel said organisations must move towards continuous and context-aware security models that combine passwordless authentication, MFA, zero trust frameworks and intelligent threat detection.
Passwordless authentication is moving into the mainstream
The industry’s preferred direction is becoming increasingly clear. On this World Password Day, they talk about fewer passwords and more passwordless systems.
Shakeel Khan, Regional VP and Country Head, Okta India, said passwords remain easy to exploit, reuse and forget, making them a persistent security weakness.
“As we mark World Password Day, the shift to passwordless authentication is no longer a future vision but a present necessity,” Khan said.
He pointed to biometrics, device-based verification and phishing-resistant passkeys as safer and more seamless alternatives to traditional passwords.
Importantly, Khan stressed that passwordless security must also extend to AI agents.
“A credential exposed through an agent carries the same risk as one stolen from a human, often with far less visibility,” he said.
This reflects a broader industry concern. AI systems are increasingly interacting with enterprise platforms autonomously, yet many organisations still lack proper governance controls around AI identity management.
India’s regulatory push is adding pressure
Another factor shaping enterprise security strategies is regulation.
Balaji Rao, Commvault, noted that evolving frameworks such as India’s Digital Personal Data Protection (DPDP) Act are increasing accountability around identity governance and access control.
That matters because identity security failures are no longer seen purely as technical incidents. They can quickly become compliance risks, operational disruptions and reputational crises.
For enterprises operating across regulated sectors such as BFSI, healthcare and telecom, stronger authentication systems are increasingly tied to board-level risk discussions.
The future of authentication will be invisible
One interesting shift emerging from the industry commentary is the idea that future security systems should become less visible to users while becoming stronger underneath.
Security teams increasingly want systems that continuously verify trust in the background rather than forcing users to repeatedly enter passwords.
That includes passkeys and biometric authentication, adaptive MFA, behaviour-based verification, device trust validation, context-aware access controls, and continuous authentication systems
The larger goal is simple: reduce friction for legitimate users while making attacks significantly harder for cybercriminals.
Conclusion
World Password Day 2026 highlights a major transition underway across the cybersecurity industry. The debate is no longer about creating stronger passwords alone. It is about redesigning digital identity for an AI-first world.
Human users are now only one part of the identity ecosystem. AI agents, service accounts and machine identities are rapidly multiplying inside enterprises, often with powerful access privileges and limited oversight.
That reality is forcing organisations to move towards passwordless authentication, zero trust security and continuous identity verification models.
For enterprises in India and across the SAARC region, the message is becoming difficult to ignore: passwords may still exist for years to come, but relying on them alone is no longer enough.
Read More:
AI data centre infrastructure India: Why storage is now critical for scaling AI
ASIRT TechDay 136: Empowering Mumbai SIs with MSP growth strategy



 2 Min read


