


 Follow Us
AI agents are starting to interact with websites, apps and customer portals in ways that look very different from traditional bots. They can complete multi-step actions such as transactions, travel bookings and banking operations, often through APIs and at machine speed. That is putting pressure on security tools built around a simple question: bot or human?
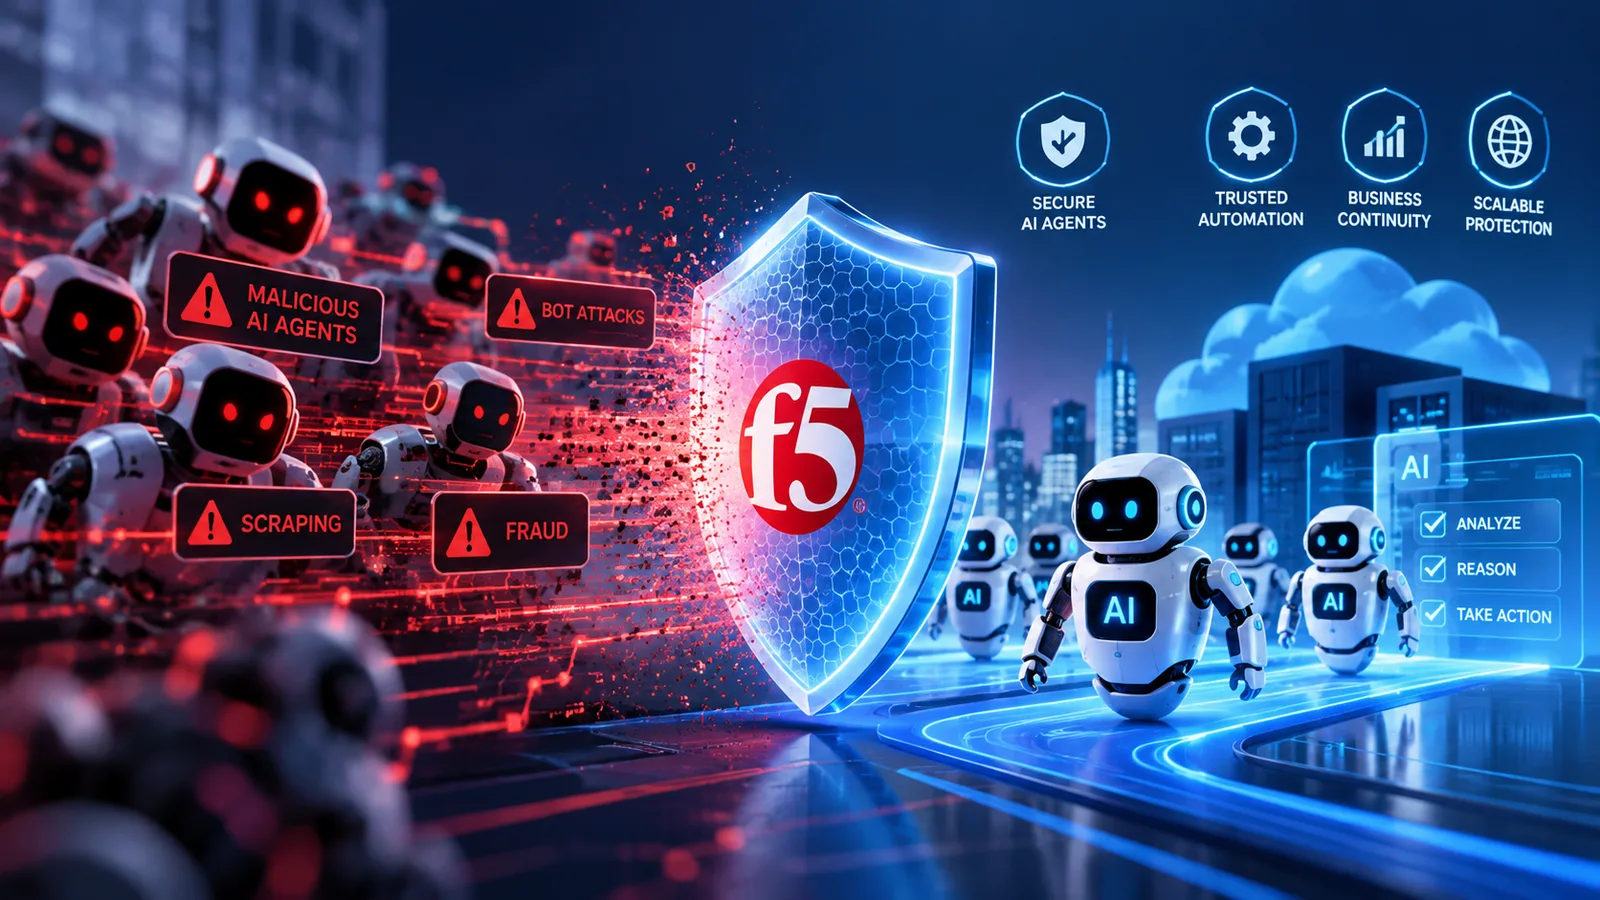
F5 is responding with new capabilities for F5 Distributed Cloud Bot Defense, combining persistent device intelligence with protections designed specifically for agentic AI. The goal is to help organisations make risk decisions based on behaviour, device context and the nature of the interaction rather than blocking automated traffic outright.
Device intelligence adds context to bot defense
A key change is the move towards persistent device context. F5 Bot Defense can identify and track devices across sessions and accounts, helping expose patterns linked to multi-account access, credential stuffing and account takeover.
Real-time device risk scoring adds another layer by examining client integrity signals and identifying environments such as emulators, spoofed devices and tampered clients. This gives security teams more information to assess whether an interaction should be trusted.
Agentic AI needs a different security model
The announcement also points to a shift in how organisations may need to approach Agentic AI detection. Traditional request-level controls can struggle when legitimate AI agents and malicious automation both interact with APIs.
F5's agent-aware policy framework is designed to classify humans, trusted AI agents and malicious bots within a single policy structure. That creates room for organisations to support legitimate AI-driven workflows while still applying controls to risky activity.
Risk decisions become more dynamic
The new approach also introduces risk-based workflow enforcement. Instead of treating every suspicious interaction the same way, organisations can apply actions such as allowing traffic, adding a step-up challenge, rate-limiting or blocking it.
This is particularly relevant to Automated account abuse, where blunt controls can create friction for genuine users. F5 says the approach is intended to reduce unnecessary CAPTCHA use and false positives while still addressing suspicious behaviour.
Read More:
Smarten Power Systems new products debut at REV Expo
Enterprise AI partners: Why domain expertise and integration now matter
Belding India expands modular data centre business into North America
SEMICON India 2026 brings 25 semiconductor agreements into focus